Kernel telemetry
Linux CN_PROC netlink process events and fanotify/inotify file activity, a Windows ETW consumer, and an opt-in macOS Endpoint Security client — with polling fallback.
v1.1.0Real kernel telemetry, Tantivy search, WASM extensions
Wardex is a private-cloud XDR and SIEM built in Rust. Detection, investigation, threat hunting, fleet operations and governance ship as one signed binary — on your infrastructure, with no telemetry egress unless you enable it.
Why Wardex
Wardex is built for security teams that need professional tooling without handing their telemetry to a vendor.
Your telemetry never leaves your infrastructure. Deploy on-prem, in your VPC, or air-gapped. Every integration — SIEM, IdP, threat feeds — is yours to configure or disable.
Rust edition 2024, MSRV 1.88. No runtime to manage, no JVM to patch, no Python toolchain drift. A single reproducible binary serves agents, API, and the browser console.
Every release ships with SLSA build provenance attestations, CycloneDX SBOMs, and cosign-signed container images. CI is SHA-pinned and secret-scanned on every push.
New in v1.1.0
v1.1.0 replaces placeholders with working engines and hardens them after a full code review. Where a capability depends on platform privileges, we say so.
Linux CN_PROC netlink process events and fanotify/inotify file activity, a Windows ETW consumer, and an opt-in macOS Endpoint Security client — with polling fallback.
/api/search and /api/hunt run on a real Tantivy index instead of an in-memory re-scan.
A native .yar compiler for a documented subset of YARA syntax, alongside the existing JSON rule format.
Random Forest triage (CART, bootstrap, out-of-bag evaluation) trained from analyst feedback, plus federated averaging with differential privacy.
Sandboxed third-party extensions on wasmi: fuel-metered, no JIT, versioned host ABI.
VirusTotal and AbuseIPDB enrichment, bidirectional Jira and ServiceNow ticketing, OTLP export, SMTP STARTTLS, Okta polling, Docker/Podman and Kubernetes event sources.
| Platform | Primary source | Verification status |
|---|---|---|
| Linux | CN_PROC netlink + fanotify/inotify, /proc fallback | CI-tested |
| Windows | ETW consumer (requires an elevated agent), polling fallback | Not yet exercised on an elevated host |
| macOS | Endpoint Security behind the opt-in macos-es feature (Apple entitlement required) | Not CI-verified |
| eBPF | Not implemented | Not available |
Platform Capabilities
One platform covering the full SOC lifecycle. Every surface is driven by the same data model and permission system.
Adaptive scoring, Sigma rules, compiled YARA rules, and kernel event telemetry feed a single per-event risk assessment.
Campaign clustering across the fleet, deception canaries, attacker profiling, and memory forensics for proactive investigations.
Queue, cases, SLAs, process trees, timelines, and storyline views keep analysts inside one investigation surface with full context.
SHA-256 baselines for critical system paths with change detection and per-agent snapshots across Linux, macOS, and Windows.
Behavioural baselines with impossible-travel detection catch compromised credentials that static rules miss.
Quarantine, isolate, and remediate with documented approvals, full audit trails, and automatic rollback on failure.
Insights
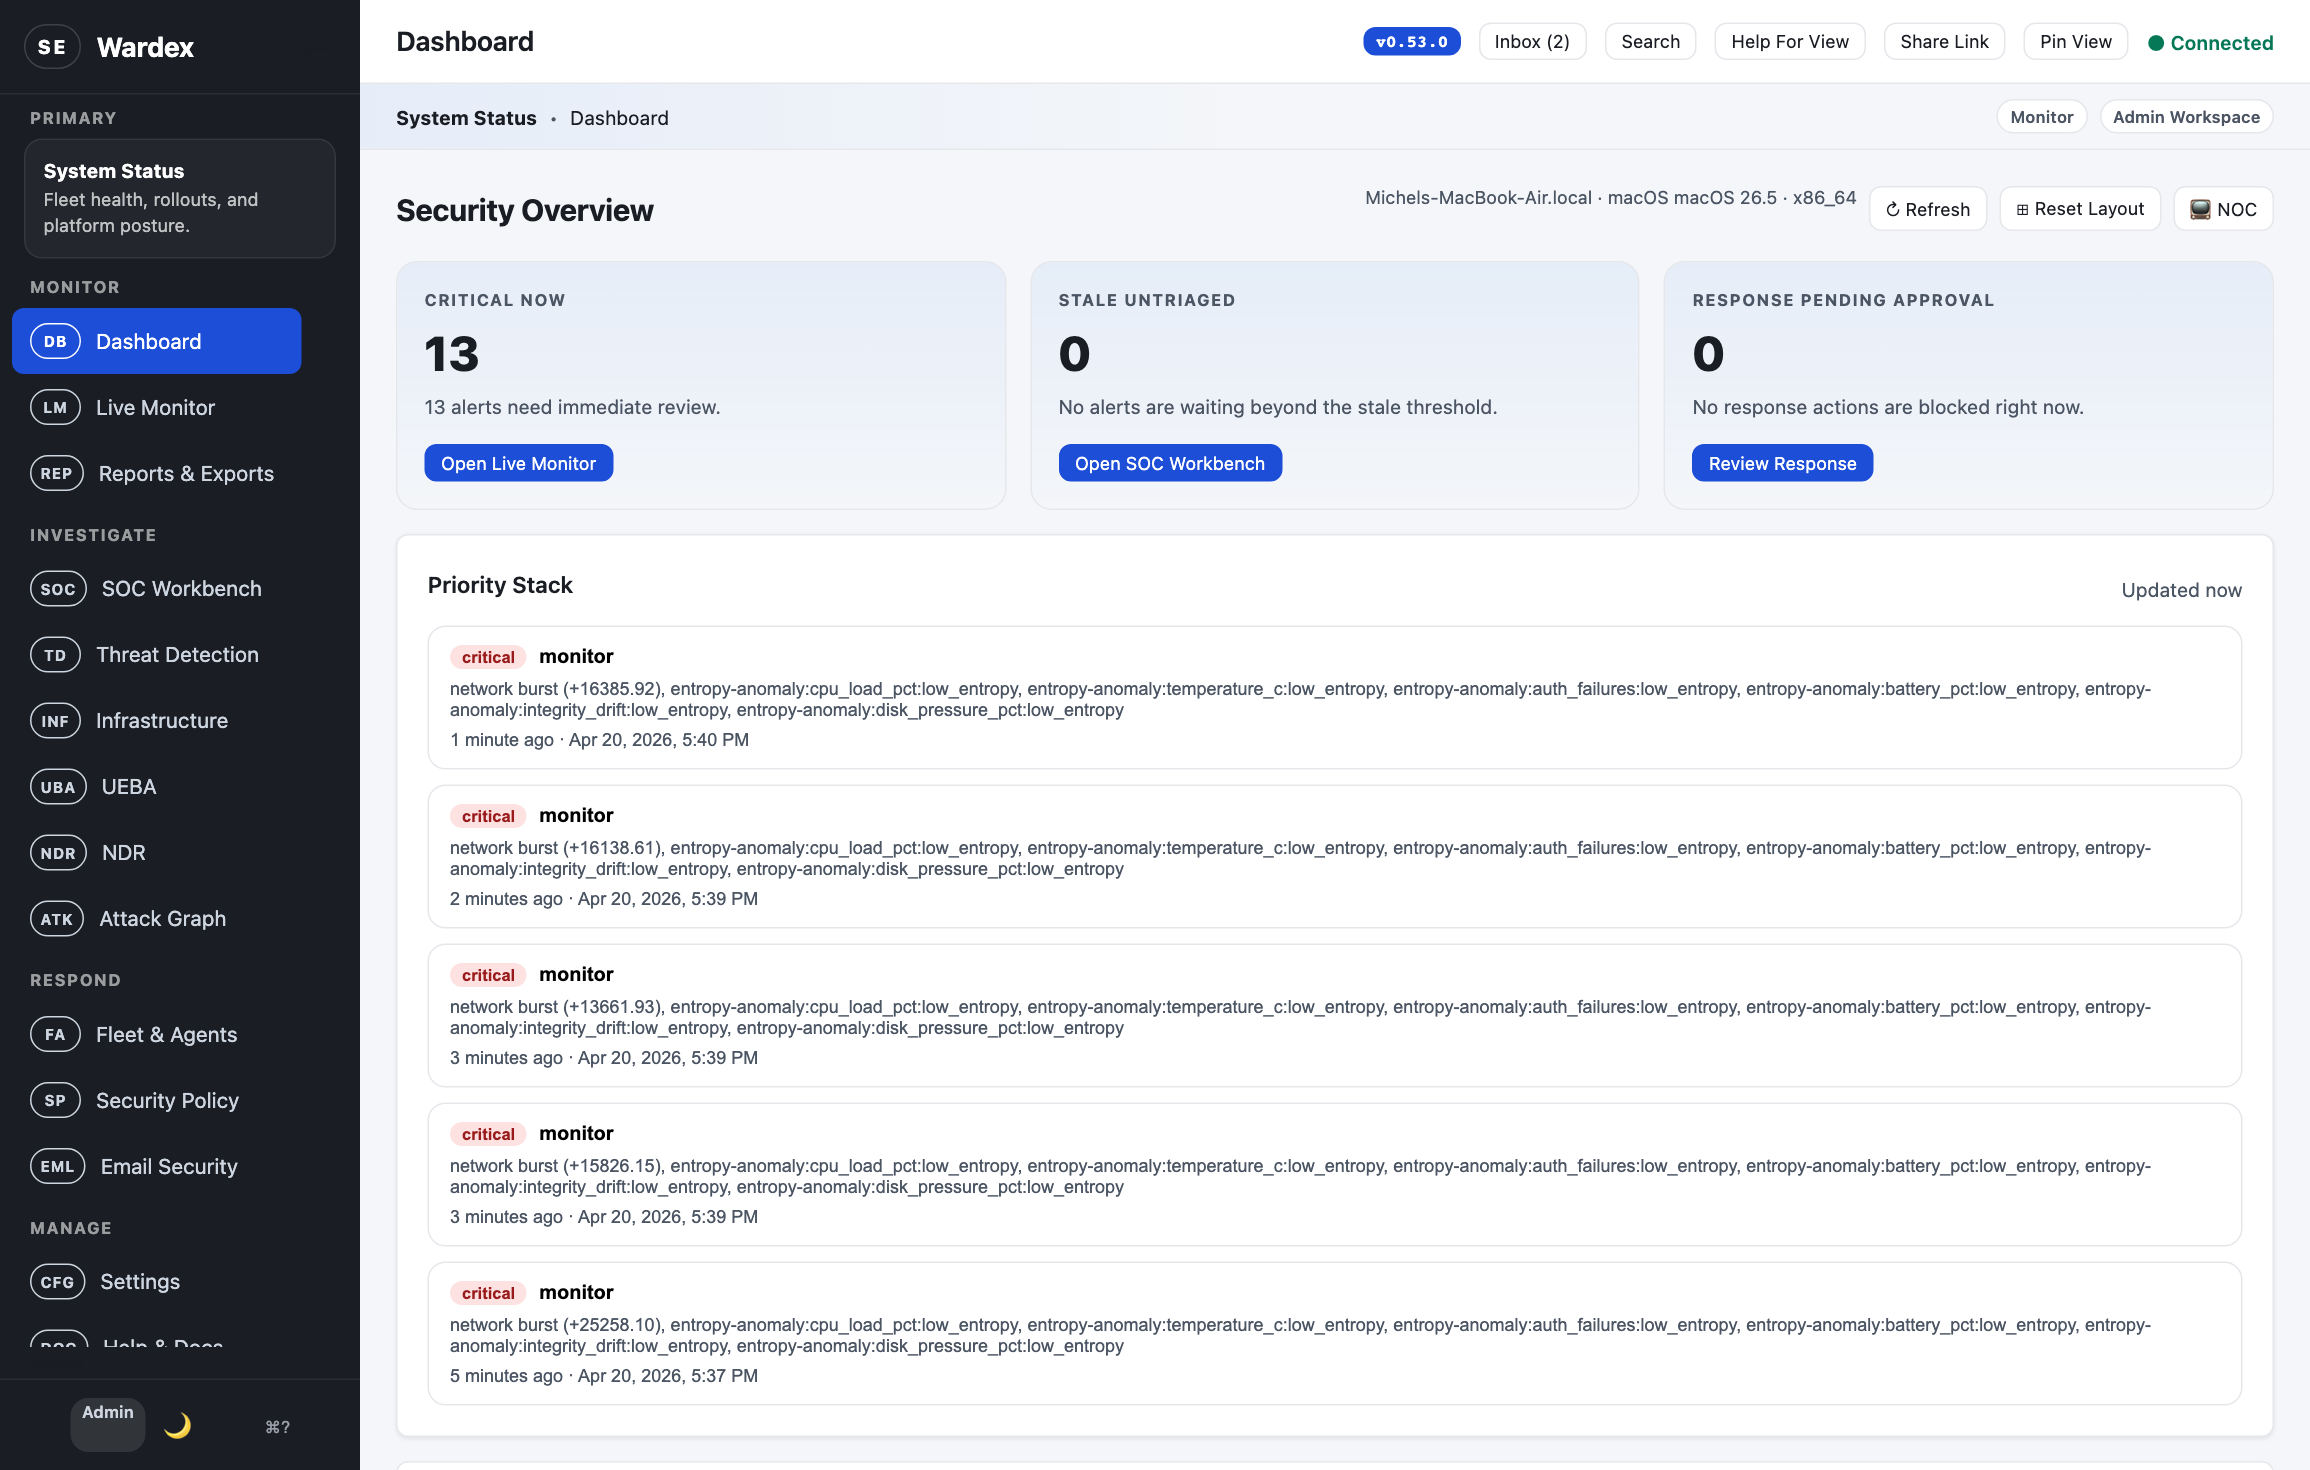
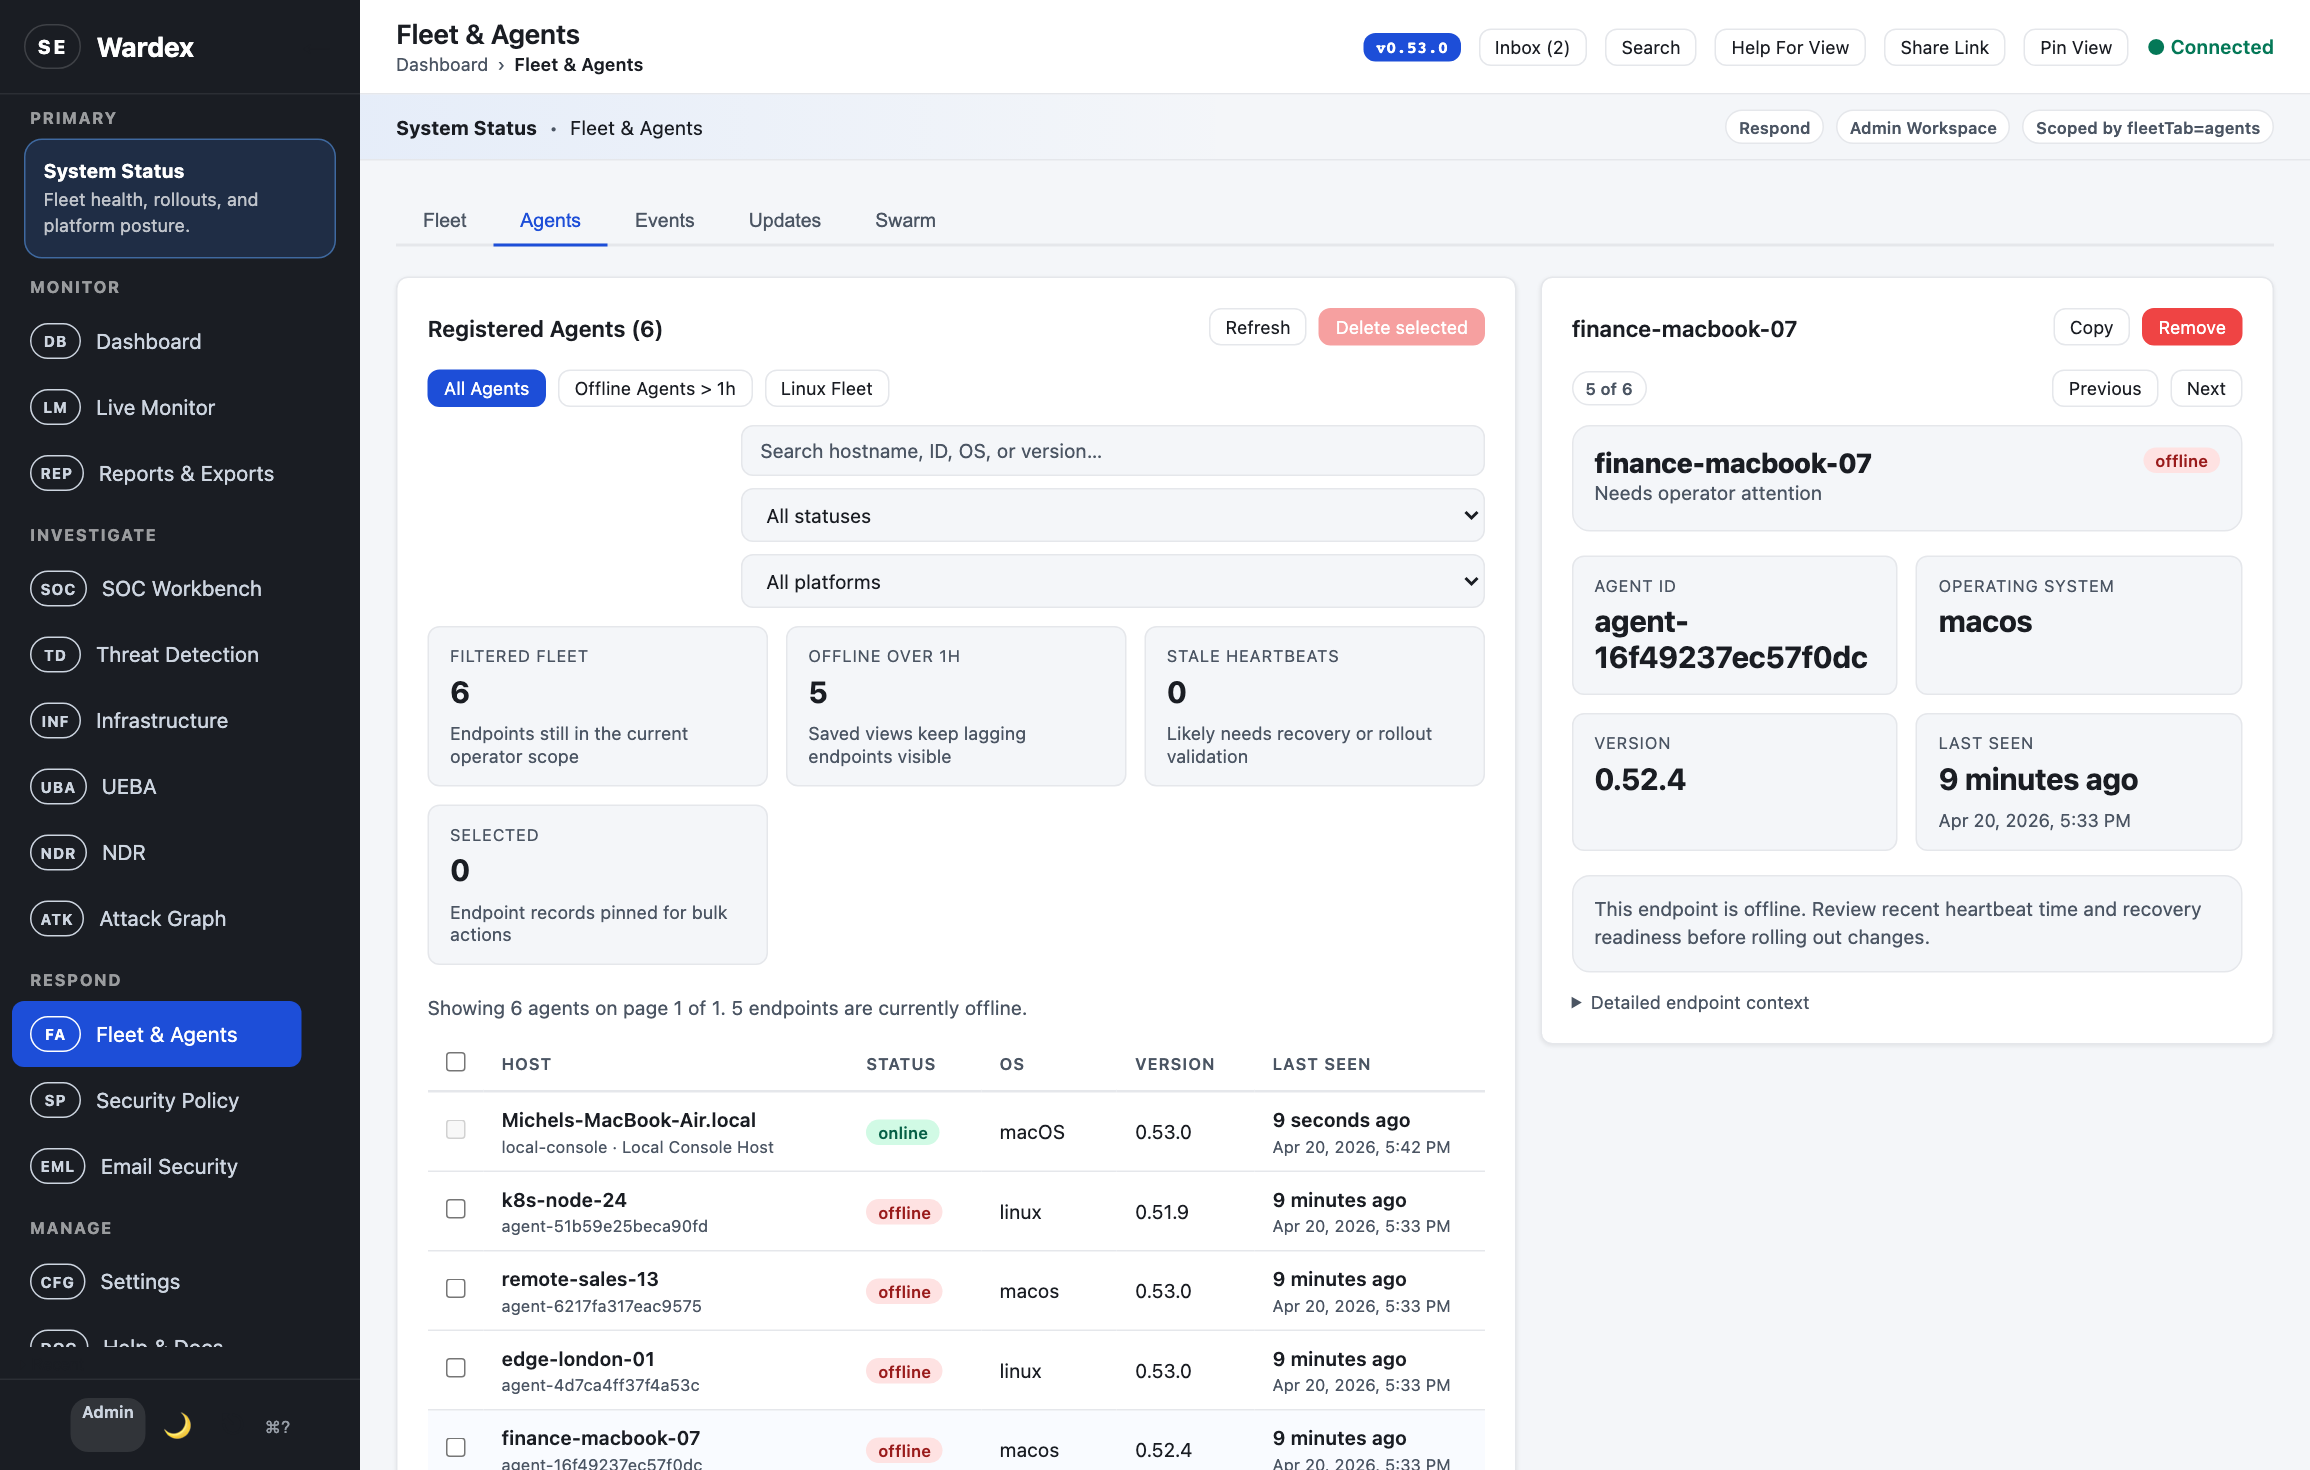
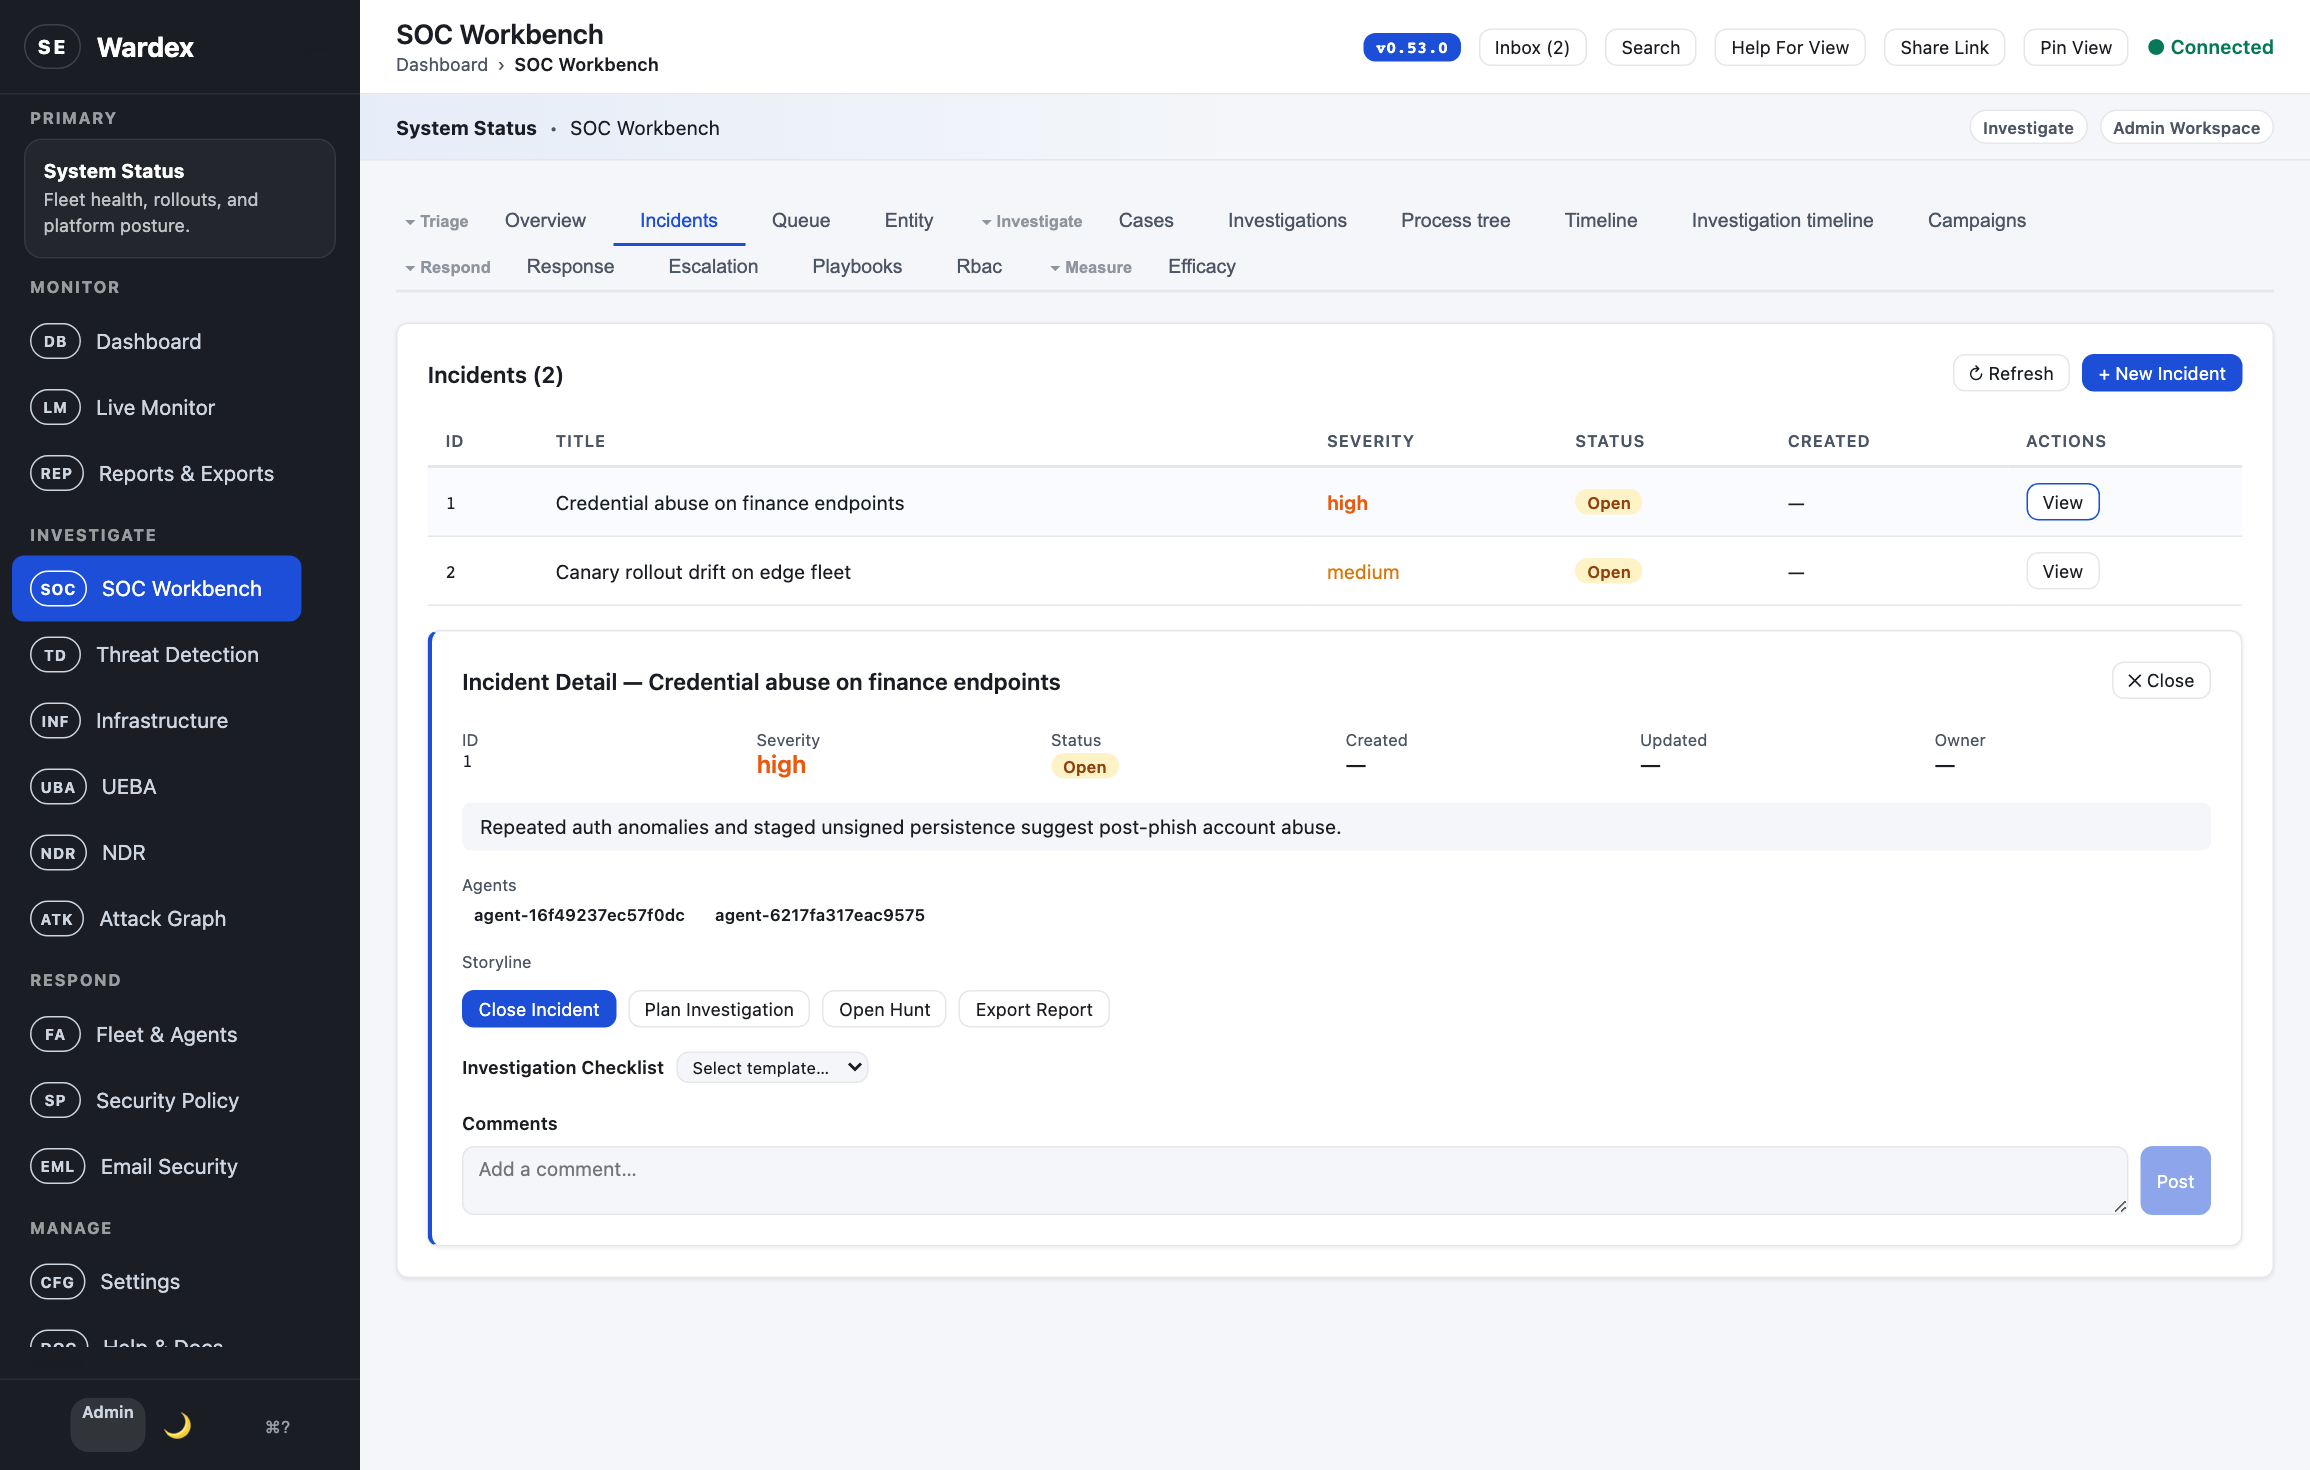
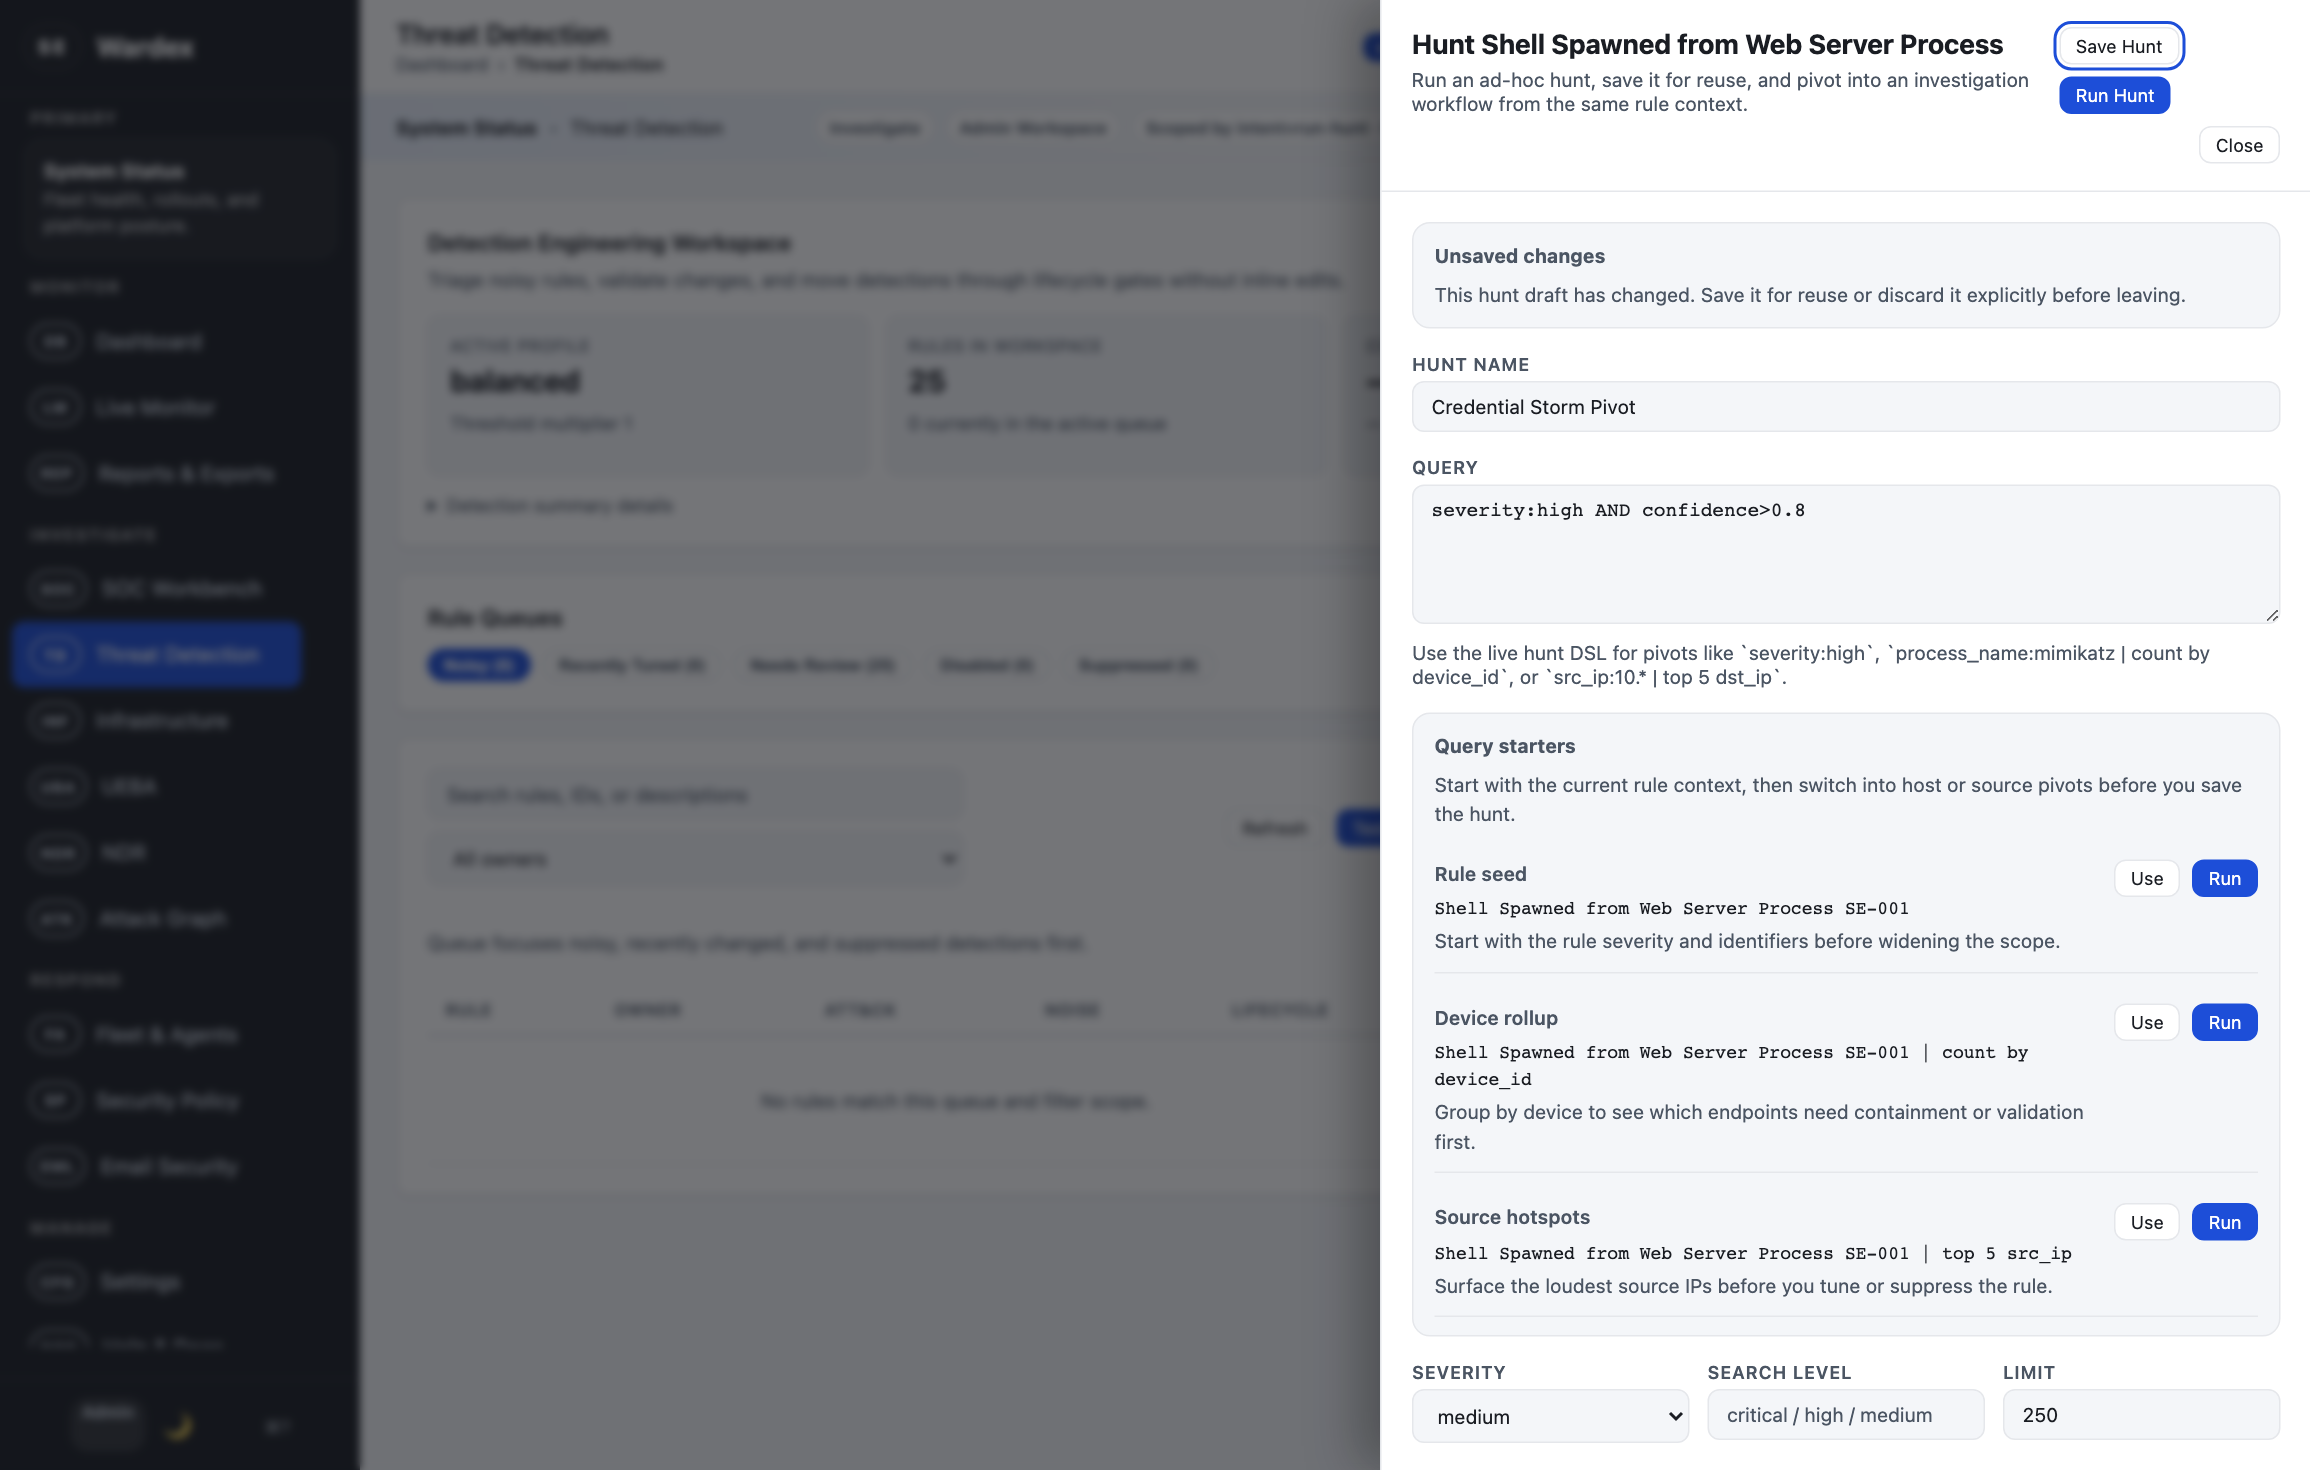
Captured from a recent local Wardex instance with seeded alerts, enrolled endpoints, active incidents, and an in-progress hunt. No static mockups.
One control plane for posture, triage, fleet recovery, and hunt workflows.
Wardex keeps detection, investigation, and endpoint operations inside the same product surface. Analysts do not have to swivel between stitched-together tools to move from an alert to a host, a case, or a hunt.
Fleet Operations
Version lag, heartbeat gaps, and endpoint detail stay visible without leaving the fleet workspace.
Incident Response
Open incidents carry linked agents, narrative context, and next-response actions inside the same SOC workbench.
Threat Hunting
Run an ad hoc hunt, reuse the query, and widen scope from the same detection engineering surface.
By the Numbers
Counts are generated from the v1.1.0 source tree and test suites.
Deploy Anywhere
Run a single binary under systemd, launchd, or as a Windows Service. Every channel below is published from the same signed release pipeline.
# Linux (Debian / Ubuntu)
$ curl -fsSL https://pinkysworld.github.io/Wardex/apt/pubkey.gpg \
    | sudo gpg --dearmor -o /usr/share/keyrings/wardex.gpg
$ sudo apt install wardex

# macOS
$ brew tap pinkysworld/wardex
$ brew install wardex

# Kubernetes
$ helm install wardex ./deploy/helm/wardex

ok ready to serve
Evaluate Wardex in your own environment today. The source code is open under AGPL 3.0 — commercially licensed for production deployments.